Asset Management for OT Environments
See every asset. Understand every risk.
Act with confidence.
OT Asset Management delivers a continuously updated inventory of industrial assets, providing the visibility needed to assess exposure, prioritise risk, and guide decisions.
Asset Discovery:
The Foundation of OT Security
Comprehensive asset discovery forms the foundation of OT cybersecurity by enabling informed decision-making and risk prioritisation.
- Complete Live Asset Inventory
- Detailed Asset Information
- Identification of Asset Vulnerabilities
- Exposure & Risk Awareness
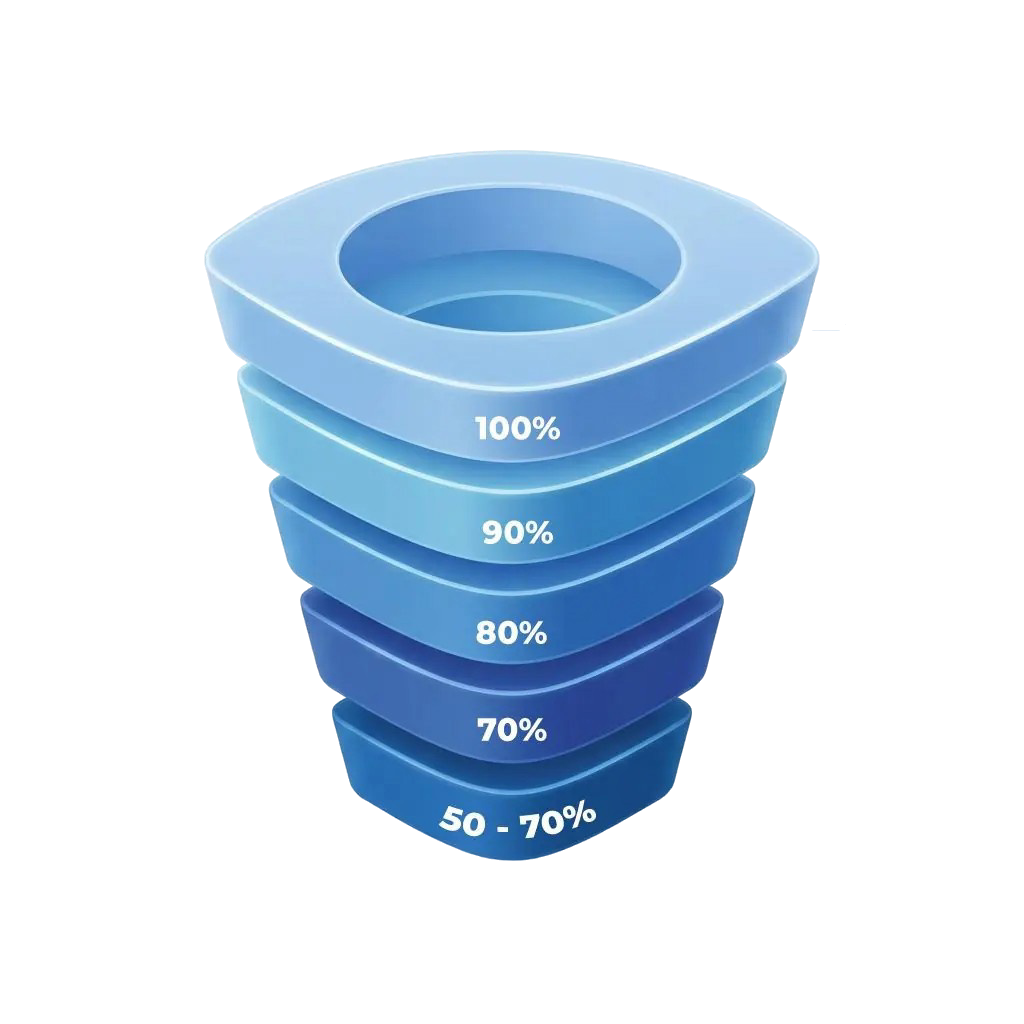
100% Intelligent Active Discovery
Intelligent Active Discovery (IAD) safely queries OT devices to capture complete asset metadata, combining passive and controlled active methods to deliver full visibility without impacting sensitive or legacy systems.
80% Active Network Scanning
Active network scanning gathers complete device metadata but impacts legacy and sensitive OT equipment due to its lack of control and protocol awareness.
50% Passive Network Discovery
Passive discovery observes network traffic to identify active devices and communication patterns, but cannot capture complete device metadata, leaving blind spots in the inventory.
90% Credentialed/Agent-Based Discovery
Credentialed or agency-based discovery provides detailed asset metadata but requires prior knowledge of credentials and significant engineering effort to configure and maintain.
70% Integration & Enrichment
Integration and enrichment leverages existing CMDBs and inventories to add context to discovered assets, but it cannot identify unknown devices on its own.
Intelligent Active Discovery
Complete, Safe, Actionable
Captures full device metadata without risking operations. Complete visibility enables accurate vulnerability assessments and informed risk prioritisation.
Stop Guessing What’s On Your Network!
You cannot protect what you cannot see. Our non-intrusive discovery identifies every legacy PLC and vendor-managed device without risking a second of production uptime.
Total Devices
New Devices (7 days)
Default Credentials
Critical CVEs
End of Life Devices
Firmware Risk
Asset Vulnerability Assessment
Identify exploitable weaknesses at the device level
- Assess device firmware versions against vendor advisories and release documentation
- Identify default, weak, or non-compliant authentication credentials
- Perform device-level vulnerability scoring using CVSS metrics
- Detect configuration weaknesses and validate certificate status
Informed Remediation Planning
Enable risk-aware, operationally safe remediation decisions
- Automated Credential & Password Management — rotate and enforce secure device credentials at scale, replacing defaults and weak passwords.
- Firmware & Certificate Management — Safely manage firmware upgrades or downgrades and automate certificate deployment, renewal, and validation to eliminate known vulnerabilities and ensure trusted device communications.
- Device Configuration Backups — Securely capture and maintain device configuration backups to enable rapid restoration, support change recovery, and improve operational resilience.
- Configuration Hardening & Drift Management — Automatically remediate risky or non-compliant configurations, detect configuration drift, and restore devices to a compliant state in line with security policies.